Maritime Cyber Security & Threats May 2020 Week Three

Vessel Impersonation Report
Red Sky Alliance, perform weekly queries of backend databases, identifying all new data containing Motor Vessel (MV) and Motor Tanker (MT) in the subject line of malicious emails. Email subject line Motor Vessel (MV) or Motor Tanker (MT) keyword usage is a common lure to entice users in the maritime industry to open emails containing malicious attachments.
With our cyber security partner we are providing a weekly list of Motor Vessels where it is observed that the vessel is being impersonated, with associated malicious emails.
The identified emails attempted to deliver malware or phishing links to compromise the vessels and/or parent companies. Users should be aware of the subject lines used and the email addresses that are attempting to deliver the messages.
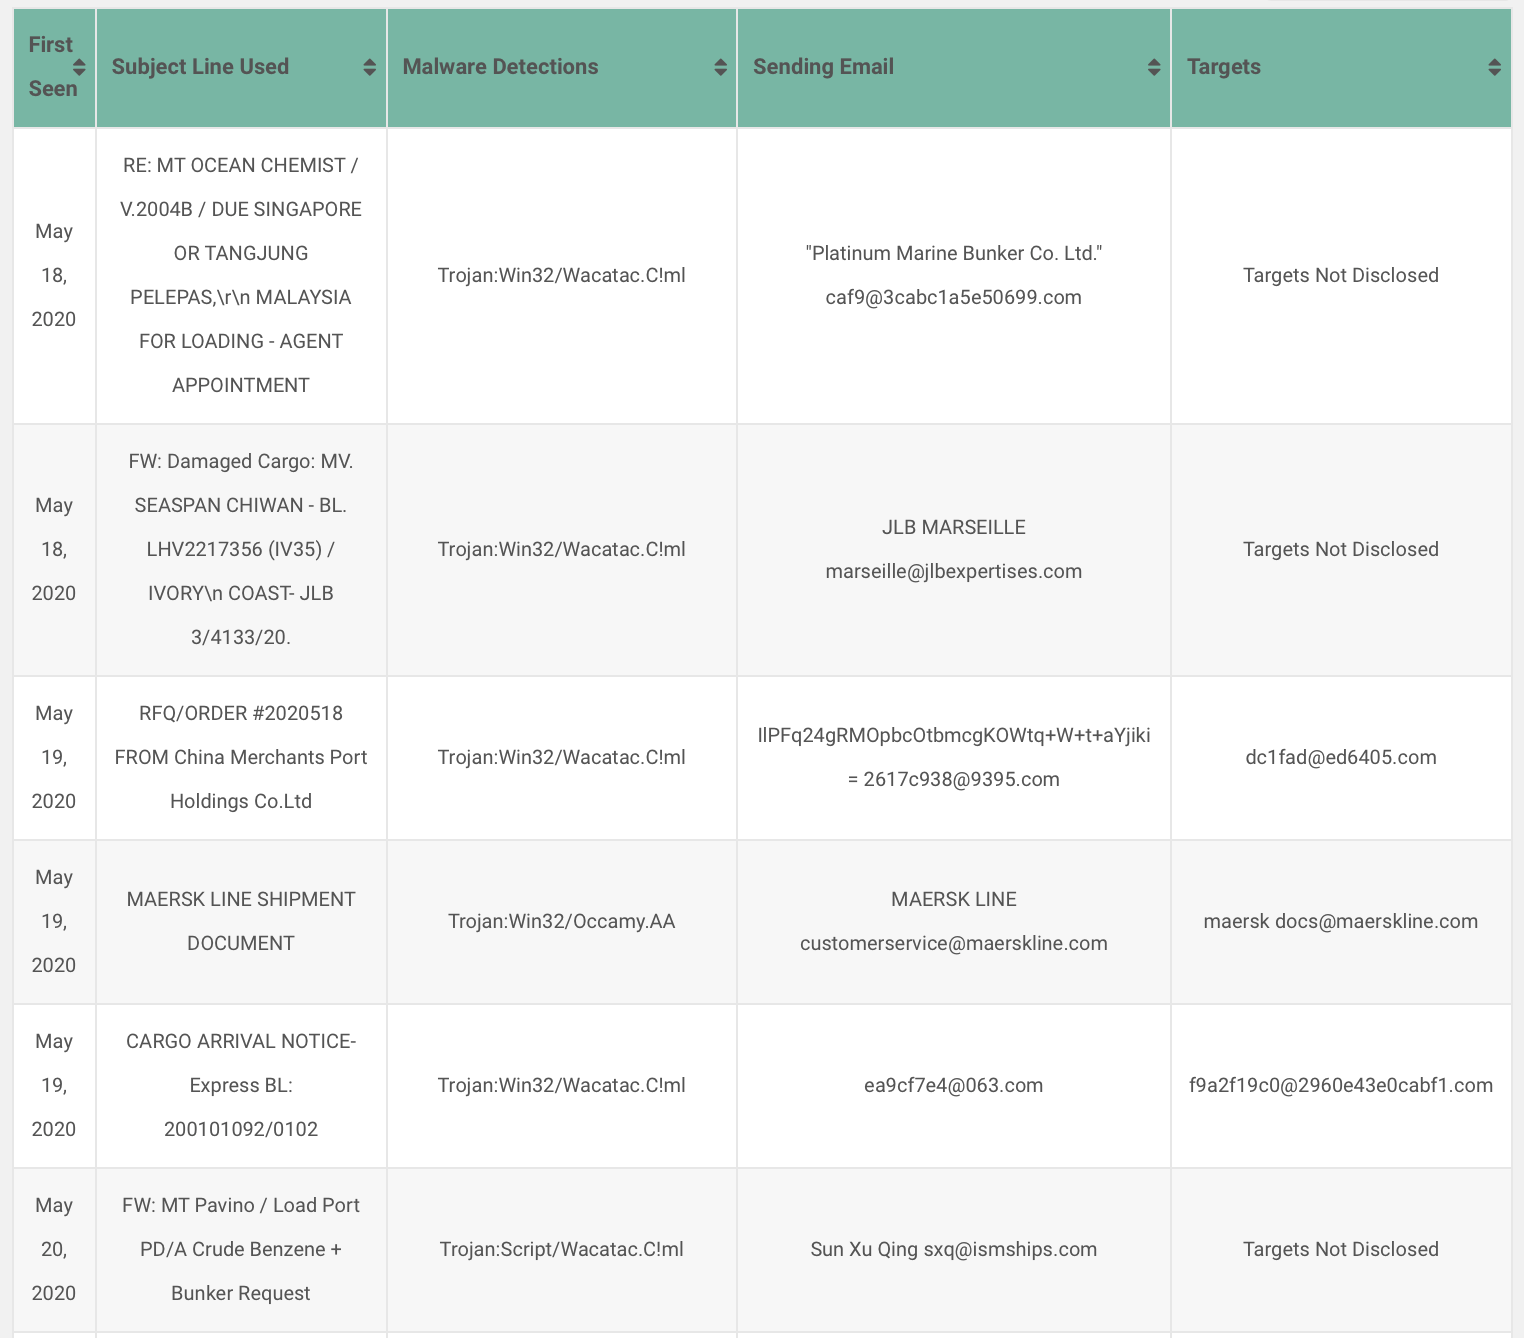
In the above collection, we see malicious actors attempting to use vessel names to try to spoof companies in the maritime supply chain. This week we observed a wide variety of maritime-related subject lines. Some of the new vessel names used this week include “MT Pavino” and “MV GOLDEN PEARL” among others.
Analysts observed subject line “M/V Ocean Adventure – Fittings for Rescue Boat Repair” being used in a malicious email this week. The malware contained in this email is one of the most common pieces of malware observed by analysts across all industries.
The email sender is listed as “li <beast3x@eliteomar.com>.” The sending email address does not appear to be registered to any legitimate company, and the domain (eliteomar[.]com) is listed on a defacement website indicating that the webhost was hacked by an Indonesian hacking team – “Indonesian Cyber Jawa”. The email signature shows the sender’s name is “Kelvin Li” and lists two maritime companies – ATN Marine and Trading Co., LTD & ARC Marine Services Co.,LTD. Notably, the mailing address listed in his signature is not registered to either company. A more legitimate email li@atn.com.cn is listed in the signature as well so it is unclear why this user would be sending emails from the “beast3x@eliteomar.com” address.
The targeted recipient of this email is an International Technical Marine Sales agent for Fuji Trading (Marine) B.V. which is a “world leader in marine supply” located in The Netherlands.[1] There is no clear connection between Fuji Trading (Marine) B.V. and ATN or ARC Marine. Hans’ email does not appear to be listed publicly anywhere online.
The malware in this email is contained in a malicious .doc attachment titled “103 SWIFT 13-05-20.doc.” When opened, the victim would activate HEUR:Exploit.MSOffice.Generic malware.[2] This malware exploits a MS Office memory corruption vulnerability (CVE-2017-11882), often downloading a malicious file disguised as an audio driver (%Application Data%\audiodrvrdll.exe).[3]
Analysts observed another malicious email containing the subject line used last week, “Amended P.O 28602 / Hebei Ocean.” The email was sent from “Hebei Ocean Shipping Agency Ltd.<agencqhd@hoscoagency.com>.”
The sender email domain appears to be registered to the Hebei Ocean Shipping Agency domain “hoscoagency.com.” As there is no company website. Analysts are unable to verify the legitimacy of the sending domain but have low confidence that the domain is in fact owned by the shipping agency. The sending email address was associated with a separate malicious email posted on a spam-email website and does not appear to be a deliverable email address.[4]
The targets were not disclosed in this email making it difficult to conclude the attackers intentions, but the malicious file attachment:
“PURCHASE ORDER 28602.gz” contains HEUR:Backdoor.Win32.Androm.gen” malware.[5] The file contains backdoor malware which makes registry and file changes to gain a foothold on the victim’s device. Kaspersky claims that approximately 25% of this malware’s victims are in either Germany or Russia.
These analytical results illustrate how a recipient could be fooled into opening an infected email. Doing so could cause the recipient to become an infected member of the maritime supply chain and thus possibly infect victim vessels, port facilities and/or shore companies in the marine, agricultural, and other industries with additional malware.
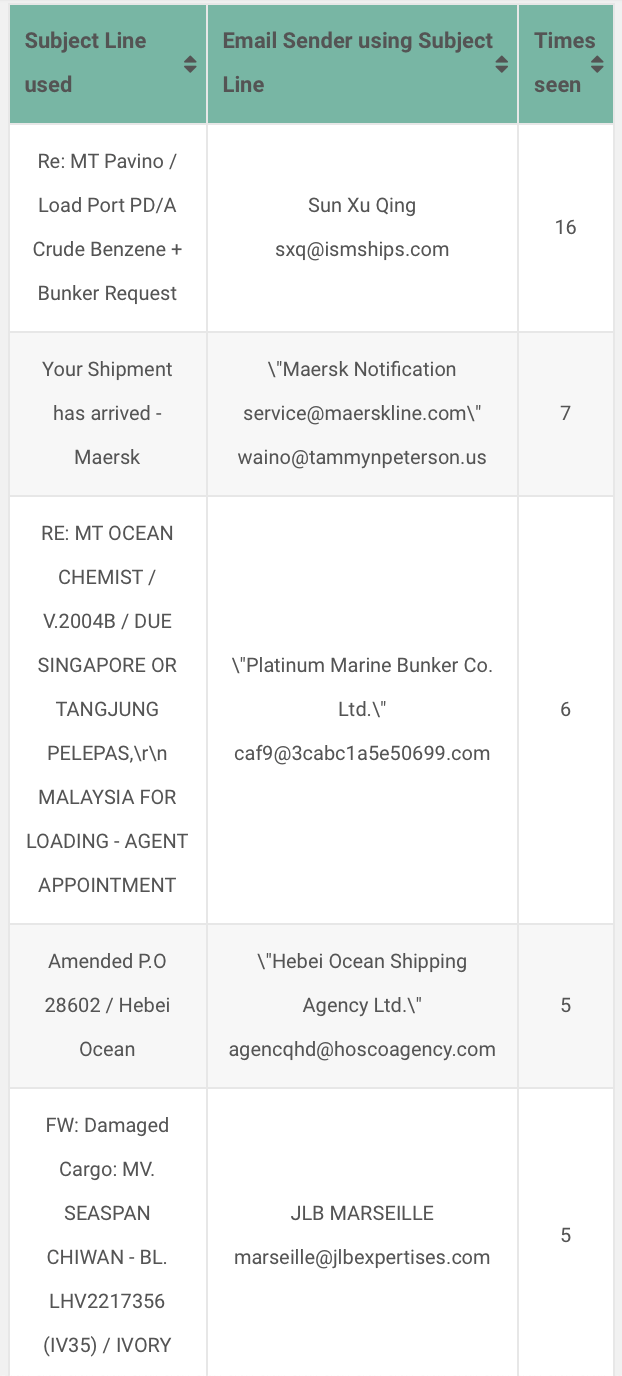
These analysis results illustrate how a recipient could be fooled into opening an infected email. Doing so could cause the recipient to become an infected member of the maritime supply chain and thus possibly infect victim vessels, port facilities and/or shore companies in the marine, agricultural, and other industries with additional malware.
Fraudulent emails designed to make recipients hand over sensitive information, extort money or trigger malware installation on shore-based or vessel IT networks remains one of the biggest day-to-day cyber threats facing the maritime industry. These threats often carry a financial liability to one or all those involved in the maritime transportation supply chain. Preventative cyber protection offers a strong first-line defense by preventing deceptive messages from ever reaching staff inboxes, but malicious hackers are developing new techniques to evade current detection daily. Using preemptive information from Red Sky Alliance-RedXray diagnostic tool, our Vessel Impersonation reports, and Maritime Blacklists offer a proactive solution to stopping cyber-attacks. Recent studies suggest cyber-criminals are researching their targets and tailoring emails for staff in specific roles. Another tactic is to spoof emails from the chief executive or other high-ranking maritime contemporaries in the hope staff lower down the supply chain will drop their awareness and follow the spoofed email obediently. Analysts across the industry are beginning to see maritime-specific examples of these attacks.
Pre-empt, don’t just defend
Preventative cyber protection offers a strong first-line defense by preventing deceptive messages from ever reaching staff inboxes, but malicious hackers are developing new techniques to evade current detection daily. Using preemptive information from Red Sky Alliance RedXray diagnostic tool, our Vessel Impersonation reports and Maritime Blacklists offer a proactive solution to stopping cyber-attacks. Recent studies suggest cyber-criminals are researching their targets and tailoring emails for staff in specific roles. Another tactic is to spoof emails from the chief executive or other high-ranking maritime contemporaries in the hope staff lower down the supply chain will drop their awareness and follow the spoofed email obediently. Analysts across the industry are beginning to see maritime-specific examples of these attacks.
The more convincing an email appears, the greater the chance employees will fall for a scam. To address this residual risk, software-based protection should be treated as one constituent of a wider strategy that also encompasses the human-element as well as organizational workflows and procedures.
Source: Dryad Global



Related News.

Navigating the Multi-Orbit Era: In Conversation with Intellian’s Jon Harrison at SMM 2026
At SMM 2026 in Hamburg, the rapid evolution of maritime satellite communications took centre stage. Across the exhibition halls, discussions among…

Cyprus ports need joint energy and investment strategy, shipping agents chief says
Cyprus needs a coordinated strategy for shipping, energy and environmental protection to support port investment and modernisation, Cyprus shipping…

MASO Public Affairs introduces MASO Regulatory Intelligence
A new subscription service helping businesses understand what is changing and what it means for them MASO Public Affairs introduces MASO Regulatory…

Anglo-Eastern helps turn CMBTECH’s ammonia ambition into an operational reality
From early feasibility study and risk-based design to newbuilding supervision, crew readiness and technical management, Anglo-Eastern drew on its…

Escalation of attacks threatens to derail recovery in Middle East oil exports
World oil demand is forecast to fall by 2.5 mb/d y-o-y in 4Q26 and 2.6 mb/d on average in 2026. As the Iran war manifests itself through restricted…

New study finds shipping pays twice its share to EU ETS earmarked revenues should triple to help build market for sustainable fuels and technologies
Shipping is responsible for around 10% of EU ETS emissions but pays almost 20% of the ETS bill. Unlike other sectors, it has never received free…

MSARC strengthens maritime mass rescue readiness through training and national live exercise off Dakar, Senegal
Joint MSARC–FHAS programme combines three days of SAR training with a national multi-agency live exercise The Maritime Search and Rescue Council ,…

Sogese report deliveries are still being delayed as container freight rates fluctuate
FOR IMPORTERS Spot rates into the Mediterranean are back at January levels, Far East to Europe reliability sits at pandemic lows, and nearly…

Glencore begins trading on Australian Securities Exchange
Glencore has begun trading on the Australian Securities Exchange under the ASX code GLC. Gary Nagle, Glencore’s CEO, said it was an exciting day for…

BIMCO Shipping Number of the Week
Suez Canal container ship transits exceed 50% of pre-disruption levels "During the first two weeks of October, weekly container ship capacity…
Subscribe to our newsletter!
if you dont want to swim alone in the ocean of news, sign up for the newsletter, and you will receive daily all the important news of world shipping!
