Industry leaders launch world’s first maritime-specific cyber vulnerabilities database
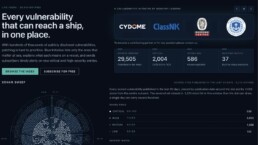

Cydome, ClassNK, Bureau Veritas, MTS-ISAC and Rakuten Maritime announce the “Blue Initiative”, an open collaboration to improve maritime cyber vulnerabilities management.
Cydome, ClassNK, Bureau Veritas, MTS-ISAC and Rakuten Maritime announced today a collaboration called the Blue Initiative to provide the first public database of cyber vulnerabilities focused only on IT and OT devices that are relevant to the maritime industry, available for free at blue-initiative.org.
With the rising number of vulnerabilities discoveries (more than 350,000 published CVEs and 200 entries added each day), identifying and prioritizing which system patches and cyber risks are relevant to each organization has become an extremely complex endeavor.
This new initiative is designed to help shipping companies more effectively address the cyber vulnerabilities affecting the specific systems and equipment they operate by highlighting maritime-related equipment, ability to focus on specific vendors, and proactively alerting users when relevant new vulnerabilities are announced.
“Identifying which vulnerabilities actually matter to the systems maritime companies operate is a major challenge”, said Cydome CEO Nir Ayalon, “and our vision with the Blue Initiative is to have a public and open single source of truth for maritime-related vulnerabilities. This will provide IT and cyber teams, vendors and research facilities a much more focused view of risks relevant to their specific vessels, making vulnerabilities and risk management much more effective and faster than before. “
The Blue Initiative is an open industry collaboration, freely accessible at blue-initiative.org. Relevant organizations in the maritime community are encouraged to join and help expand the database.
“Effective vulnerability management starts with knowing which issues matter to the systems you operate. By focusing on maritime IT and OT equipment and bringing the community together to validate the data, the Blue Initiative gives shipping companies a practical, trusted resource. ClassNK is proud to be a contributing partner,” said Naoki Saito, General Manager, Ship Management Systems Department at ClassNK
“Cyber resilience requirements for ships are not simply a checklist for audits, but a continuous process throughout a vessel’s operational life. Owners are expected to maintain the security of onboard systems as new vulnerabilities emerge, making effective vulnerability management a critical element of maritime cyber resilience. In practice, this can be challenging, as relevant information is often scattered across general-purpose databases and vendor advisories. Bureau Veritas sees real value in a shared, maritime-specific reference that owners, equipment manufacturers and class societies can all rely on. We are pleased to join the Blue Initiative as a contributing partner,” said Panagiotis Anastasiou , Cyber Technical & Market Leader, Bureau Veritas Marine & Offshore.
“Amid a shifting threat landscape where technological advancement increasingly empowers threat actors targeting maritime critical infrastructure, The Blue Initiative delivers essential vulnerability intelligence that addresses a critical vulnerability gap. Recognizing the value of this community-driven approach to maritime situational awareness, the MTS-ISAC strongly endorses this collaborative model and has integrated its operational workflows to both contribute to and leverage this vital initiative,” said Christy Coffey, VP Operations at MTS-ISAC.
“Cybersecurity must be managed across a vessel’s entire operational lifecycle, from design through operation. As a provider of maritime cybersecurity, compliance, and digital solutions, Rakuten Maritime knows that tracking equipment vulnerabilities is critical to keeping connected fleets secure. By turning complex threat intelligence into actionable protection, the Blue Initiative gives operators the trusted reference they need, and we are proud to be a contributing partner,” said Ryan Son, Managing Director of Rakuten Symphony Singapore & Korea and Head of Rakuten Maritime.
Entries in the new Maritime Vulnerabilities Repository (MVR) are reviewed by cyber researchers from Cydome and the contributing partners, who validate and refine them before going live. Select entries also receive more elaborate analyst notes, and users will be able to:
- Browse vulnerabilities and their details
- Filter vulnerability searches to the equipment or vendors relevant to them.
- Access expert insights on vulnerabilities and their impact (select vulnerabilities, with more insights constantly added every day).
- Subscribe for updates and alerts on new vulnerabilities.
“In most cases, vulnerabilities are only published once a patch is available, in line with standard responsible disclosure processes,” said Ayalon. “But the Blue Initiative links this intelligence to the specific vendors and systems that maritime users operate, allowing them to move quickly to patch and mitigate.



Related News.
Beyond Compliance to Uninterrupted Operations: Delia Shipping’s Konstantinos Stais on Maritime Cyber Resilience, LEO Expansion, and AI Governance
As the global maritime industry navigates an era of intense digital acceleration, the traditional boundaries separating shipboard operational…
Chinese AI quietly writes hackable code for Beijing’s Adversaries, even when run locally, study finds
Qwen3-Coder wrote hackable apps 19% more often for US defense contractors and leaked data 28% more often for Hong Kong activists, AI security firm…
Businesses increasingly adopt AI for cybersecurity while individuals expand privacy protections
As cyber threats grow and digital technologies become more pervasive, businesses are increasingly using AI to strengthen…
EmissionLink calls for EU ETS revenues to fund maritime carbon capture trials and port infrastructure
Maritime emissions specialist, EmissionLink, has called for a dedicated proportion of EU Emissions Trading System (EU ETS) revenues to be invested…
Port of Antwerp-Bruges sees strong recovery in container throughput in volatile trading environment
In the first nine months of 2026, Port of Antwerp-Bruges handled 200.9 million tonnes of goods, 0.8% less than in the same period last year.…
Sanctions risks reshape commodity trading
Traders face sanctions challenge “odyssey” as geopolitical risks reformat global markets Commodity traders are operating in an increasingly…
Titan analysis shows FuelEU pooling propelled liquefied biomethane demand
- Clean fuel supplier evaluates compliance for 8,000 TEU containership operating in Northern Europe - FuelEU Maritime balances competitiveness…
Russian diesel tanker heads to New York as Kremlin claims regular shipments
Malta-flagged tanker should carry 40,000 mt fuel Agioi Fanendes left Primorsk Oct. 22: CAS US lifts sanctions, enables Russian imports……
Pilot transfer operation: A safer step aboard
Safe pilot transfer operations depend on both correct procedures and fit-for-purpose equipment. New SOLAS requirements entering into force in…
Khalifa Port rises five positions to 34th in Lloyd’s List Top 100 Container PortsRanking
Khalifa Port records highest year-on-year throughput growth among the world’s top 40 container ports in the 2026 ranking Abu Dhabi’s flagship port…
Subscribe to our newsletter!
if you dont want to swim alone in the ocean of news, sign up for the newsletter, and you will receive daily all the important news of world shipping!
